WebAssembly on the server: hype or future?
Wasm escaped the browser. Is it the next container?
Wasm escaped the browser. Is it the next container?
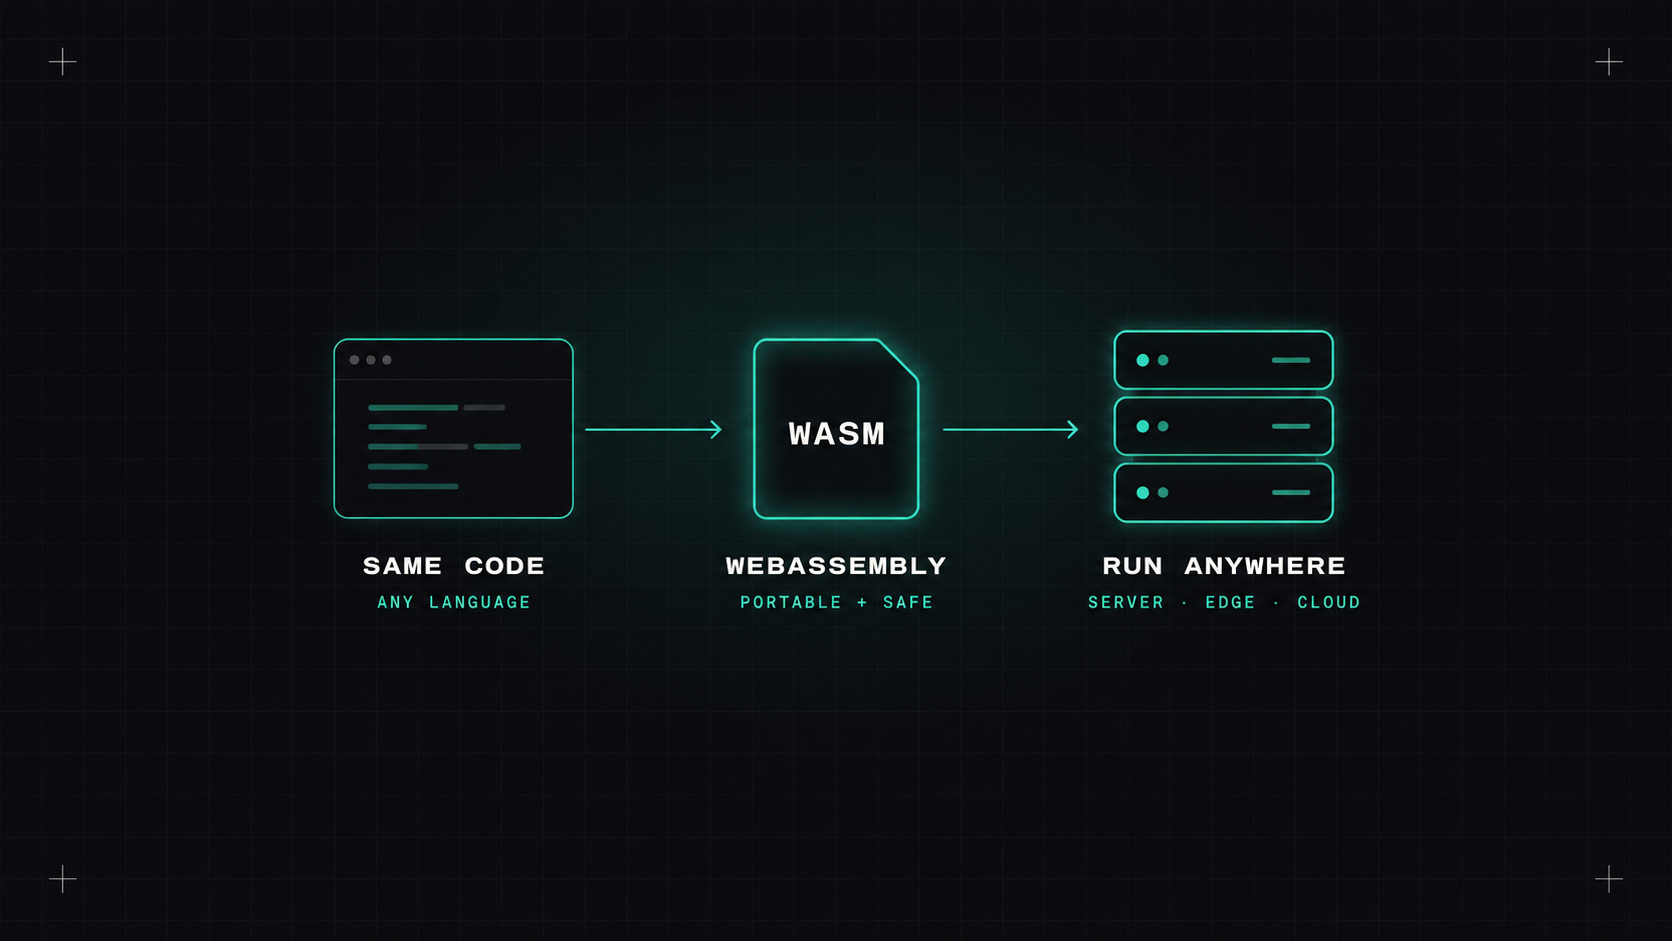
In 2019, Docker co-founder Solomon Hykes posted something that's been quoted ever since: if WebAssembly and WASI had existed in 2008, they wouldn't have needed to create Docker. That's a big claim. Several years later, where does server-side WebAssembly actually stand?
WebAssembly (Wasm) started as a way to run fast, compiled code in web browsers: games, video editors, design tools. It's a compact binary format that many languages (Rust, C/C++, Go, C#, Zig, and others) can compile to, and that runs in a sandboxed virtual machine.
The properties that make it great in browsers turn out to be interesting on servers too:
To work outside the browser, Wasm needs a way to talk to the system: files, clocks, sockets. That's WASI (WebAssembly System Interface). WASI 0.2 introduced the Component Model, which lets Wasm components written in different languages work together through well-defined interfaces. Further versions are adding async support and more.
Containers package an operating system around your app. Wasm packages just your app, and asks permission for everything else.
Wasm doesn't have to replace your platform. It can run alongside containers:
RuntimeClass. A pod can run a Wasm module instead of a container image.apiVersion: node.k8s.io/v1
kind: RuntimeClass
metadata:
name: wasmtime-spin
handler: spin
---
apiVersion: apps/v1
kind: Deployment
metadata:
name: hello-wasm
spec:
replicas: 3
selector:
matchLabels: { app: hello-wasm }
template:
metadata:
labels: { app: hello-wasm }
spec:
runtimeClassName: wasmtime-spin
containers:
- name: hello
image: ghcr.io/acme/hello-wasm:1.0.0
command: ["/"]
Wasm is already in production in places you might not notice:
Both, honestly. Wasm won't replace containers for most workloads any time soon. Containers solved a huge problem and they're everywhere. But Wasm is clearly the future for specific areas: edge, plugins, high-density serverless and safe execution of untrusted code. Those areas are growing.
For DevOps engineers, it's worth understanding now: how it runs on Kubernetes, how it's packaged in OCI registries, and where it might show up in your stack.
My take: Wasm isn't the next container. It's the thing you'll reach for when a container is too heavy, too slow or too trusting.
— Desly